Showing posts with label News. Show all posts

This Game Turns Google Autocomplete Into A Game Of Family Feud

Screen Shot 2015-03-14 at 11.07.14 AM

Damn, this is more fun than I would’ve expected.
Do you ever type things into Google just to see what whacky stuff pops up in the autocomplete box?
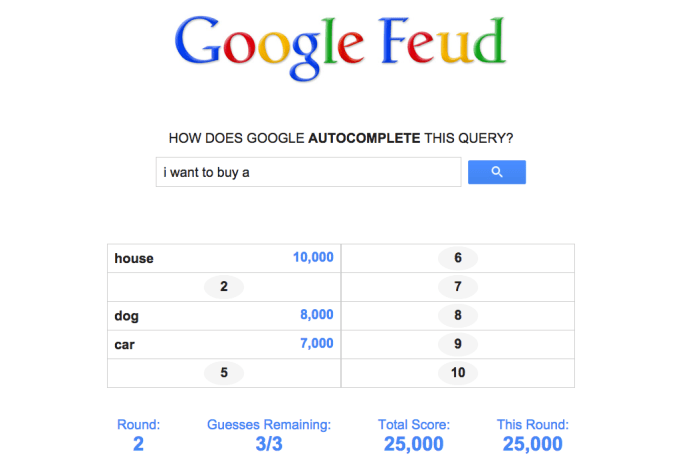
GoogleFeud takes that concept and turns it into a Family Feud-style game. How well do you know the hivemind?
GoogleFeud provides the first half of a search query, and you fill in the rest. Your goal is to guess as many of the most popular queries as you can.
If it provides “Should I sell my ….”, for example, you might guess “house”, “car”, or “dog”. If your guesses line up with one of the most popular queries as searched for by Google visitors, you get a point; if it doesn’t, you get a strike. Three strikes, and the game is over. Want to see the answers to that board up above, for example? Here you go.
One downside I’ve noticed: the engine isn’t very good at combining similar results, something that the real Family Feud accounts for behind-the-scenes. You also have to be absolutely specific in your answers — if you say “plane” and the answer was “airplane”, that’s a strike.
Quirks aside, it’s a damn fun way to kill a few minutes and see how well you can predict the wonderings of the masses.
You start off by picking one of four categories: Culture, People, Names, and Questions. I’d recommend starting with names, as it seems to be the least susceptible to the aforementioned shortcomings.
Bonus tip: there’s no built-in multiplayer option, but it’s still a pretty great game to play cooperatively with a friend. I spent the morning brainstorming guesses with my fiance — and while the game totally kicked our ass, we had a blast.

Website Hackers Slip Under The Radar With Impersonator Bots


It was late December when we were contacted by a financial service provider who began noticing a spike in online registration requests. Rather than resulting from end-of-the-year sales efforts, this spike was caused by a targeted spam attack that flooded the organization with fake registration forms, most of which looked reputable enough not be discarded on sight.
The reason for concern was that this company, for internal reasons, needed to perform a manual background check of each new registration form before it was passed over to the sales department. So when the small background check team began to collapse under the deluge of seemingly legitimate online forms, all online sales operations were brought to a halt. After a quick examination of the company’s website traffic, it quickly became clear that what the customer was actually experiencing was malicious bot activity.
In this case, the bot operator knew enough about the organization to identify the manual background check process as a “soft spot,” which could be used to monkey-wrench the company’s entire sales funnel.
To exploit that weak spot, the perpetrator hand-crafted a spam bot whose sole purpose was to attack that one specific registration form with details that wouldn’t fit any easily identifiable pattern. Most concerning, these bots were disguising themselves as regular human users, with browser-like HTTP fingerprints and several capabilities that enabled them to circumvent the website’s challenge-based, access-control mechanism.
This is not the first time we’ve come across such sophisticated bots that are purpose-built to mimic human behavior and operate under the cover of a browser-like identity. Collectively, we like to refer to them as “impersonator bots.” Created for stealth and preferred for their ability to bypass commonplace security measures, such automated tools are used by hackers not only for spam attacks, but also to steal data, hijack servers and execute DDoS attacks, among other nefarious activities.

Who are these Impersonator bots?

Many types of bad bots roam the Internet, from scrapers and spammers to the more sophisticated vulnerability scanners and DDoS bots. If other bad bots can be compared to well-trained soldiers carrying out the orders of their commander, impersonator bots are the Special Ops unit. These “commandos” carry out the same malicious activities, but they do so covertly and typically use much more advanced attack techniques.
Often, they’re based on existing malware tools, modified to create a browser-like HTTP fingerprint. This lets them bypass security challenges that would stop a lesser/generic version. Impersonator bots cause significant damage to companies’ websites and web applications, resulting in downtime, financial losses and reputation damage. 
Between 2013 and 2014, we saw overall bot traffic volumes decrease from 61.5 to 56 percent of all web visits — a reversal of the upward trend observed the prior two years. Still, despite the dip in total bot traffic, the number of impersonator bots continues to grow.
In fact, over the past three years, impersonators are the only bad bot type to display consistent growth, which does not bode well for most website owners.
Cybersecurity is often described as an arms race, and for a good reason. Hackers and white hats are continually trying to stay one step ahead of each other. When one side finds a better method of defense, the other side usually develops a smarter type of offense. Impersonator bots are a byproduct of this escalation – they are the hacker’s response to an increased use of anti-bot solutions by website owners. 

Impersonator bots are the go-to tool for hackers 

One way impersonator bots are used is for vulnerability scanning and automated hacking attempts. Such “hacker bots” are proprietary tools and scripts are used to systematically scan sites for vulnerabilities and exploit them at will and in bulk. As soon as a vulnerability is published, the scavenger hunt for an un-patched system is on.
We saw an excellent example of this dynamic following the discovery of the Shellshock mega-vulnerability in September 2014.
Soon after Shellshock’s discovery and the release of a patch, we saw an explosion in scanner traffic. Some of these were legitimate scanning attempts by concerned Internet citizens. However, more than 90 percent of the bots were malicious scanners and other malicious automated tools (e.g. DDoS malware) probing for the Shellshock vulnerability.
For hackers, launching such vulnerability-scanning campaigns is just “another day in the office.” We’ve seen this same dynamic following other major vulnerabilities in 2014, such as Heartbleed, and vulnerabilities in popular WordPress plug-ins like Slider Revolution and FancyBox.
This genre of impersonator bots also covers DDoS bots coming from anonymous proxies, which are simply another way for attackers to mask their true identities. This is the same MO used by impersonator bots. In fact, over the past few months, we’ve seen a significant increase in bots using TOR and other publicly available anonymous proxies to perform application-layer DDoS attacks (e.g. HTTP floods). These proxies were created to enable anonymous web browsing — substituting a users’ IP address with that of an untraceable proxy.
The use of anonymous proxies (most of which are free) holds many benefits for DDoS attackers. This enables them to mask their bot IPs, letting them bypass security solutions based on blacklisting. Rather than using a single address for each bot request, anonymous proxies spread requests among multiple IPs, permitting them to fly under the radar of rate-limiting mechanisms.
In addition to hiding IPs, anonymous proxies also obfuscate header information, enabling them to evade security measures based solely on HTTP fingerprinting. Utilizing these inherent benefits, perpetrators are able to create a large botnet-style impact with minimal effort.
As malicious bots evolve and become more stealthy, it’s no longer enough to know who the visitor is (i.e., block by signature). Security solutions also need to assess why any bot is there in the first place. The use of reputation and behavioral analysis can help examine the context of bot visits, which is an important factor in identifying Impersonators, anonymous proxies and other new types of bot threats.

YC-Backed Cleanly Offers On-Demand Laundry Delivery In NY

Laundry is truly one of the pain points of living in New York City. No one wants to spend their time at a laundromat, waste time dropping off dry cleaning, or lugging a bag full of clothes up to the fourth floor of a walk-up apartment.
But finding a laundromat nearby that offers fair pricing as well as pick-up/drop-off can be difficult. YC-backed Cleanly wants to change that.
Cleanly’s mobile app offers on-demand laundry pick-up in less than 30 minutes with a 24-hour turnaround. Here’s how it works:
Cleanly partners with mega cleaners in various neighborhoods who handle the actual washing, drying and dry cleaning, while Cleanly hires out its own drivers to handle deliveries.
The drivers have a back-end version of the app that lets them see where and when people are expecting pick-ups and deliveries. This allows cleaners to offer delivery through Cleanly if they so choose, but more importantly brings your laundry into the 21st century.
We have smart watches and smart washing machines and smart phones, but if you live in New York, chances are you’re still doing laundry like a college student who just moved to the big city. Cleanly envisions a world in which the user shouldn’t have to drag their stuff to the local cleaners or even haggle over the phone about the pick-up/delivery schedule.
While the added convenience of Cleanly is clear, that convenience still costs. Cleanly charges a flat $1.50/lb for regular laundry and prices out dry cleaning on a per-item basis, which is slightly higher than the prices you see at most NY cleaners. Luckily, a full breakdown of your bill is saved in the app, as well as a full history of your past laundry transactions.
Cleanly is currently available in various zip codes in New York and is focused on expanding throughout the city entirely. Learn more about Cleanly here.

Staying Relevant In A Rapid Innovation Era

Editor’s note: Brian Kelly is the chief technology officer of Golgi, a mobile cloud service for app connectivity and intelligent data transport that helps developers eliminate long loading times for connected devices and mobile apps.
Developing software today can feel like running a race. In both cases, you run into obstacles and have fierce competition charging up fast behind. Developers are faced with a living, breathing, system of technology that is constantly changing and hard to control. This is why developers need to create a system of professional retraining.
Similarly to how decathletes are constantly retraining to stay in shape for their next competition in the hopes of being named the “world’s greatest athlete,” developers must constantly retrain themselves or risk becoming a dinosaur in an era of constant disruption.
There are scores of programming languages out there, and it’s not uncommon to find different development teams working on different operating systems within the same company. Developers can no longer just write programs that someone will install, sit down at a computer, and use. Americans own, on average, four digital devices. Not only do they constantly switch back and forth between them, but they also expect high-quality, consistent experiences across them. High demand for social features and integrations throws additional wrinkles into the process, as well.
At the same time, development has never played a more critical role in driving an organization’s progress. Success requires developers and their teams to adapt fast. Below are strategies for navigating this complicated, sink-or-swim world of development

Invest in Retraining Yourself

Many professions, like teaching, medicine and law, require practitioners to take annual classes that keep their skills sharp and introduce them to new thinking or advancements in the field. Few professions change as rapidly as software development, which makes a continual commitment to learning critical for success. Within five years (or fewer), the landscape completely changes, and any developer that doesn’t take the time to retrain themselves with new skills will soon become obsolete.
A good strategy for avoiding technical obsolescence is to create a syllabus for your own personal development and stick to it throughout your working career. The syllabus can include big chunks of learning, such as Apple’s new Swift language, as well as small ones, such as sharpening up your bash scripting skills. Fortunately, the Internet holds a wealth of resources that makes continued education accessible and convenient. Lynda.com, Function Space, Udemy, Codeacademy, Code School are all good options. A little bit of training and practice a few times a week will go a long way.

Keep Notes

We’ve all heard the admonition about reinventing the wheel. Why waste time doing something from scratch when it’s already been figured out? However, this happens far too often with developers who don’t write things down. Developers are notorious for their reluctance to write documentation, but the audience here is yourself.
When you figure out something difficult, write down your results and keep them in a notes folder. Then, when you need to do something similar many months later, your recorded notes will give you a head start. You won’t have to reinvent the wheel. There are a number of online services or you can use good-old-fashioned pen and paper. In either case, remember to write down the project and date (and even color coding if you want to get really fancy) to keep all those thoughts organized. The best developers make their notes folder public and share it with their colleagues.

Read StackOverflow

StackOverflow is the only game in town for asking development-related questions, and it contains a gold mine of information for developers. The site was co-founded by Joel Spolsky after he made a bundle as a developer with Microsoft. Those days of Microsoft making millionaires out of developers are over, but Joel and co-founder Jeff Atwood have put something really important back into the industry. StackOverflow is an invaluable resource for learning, thinking about what you learn, and connecting with other members of the developer community.
Granted, not everyone loves StackOverflow. A developer named Michael Richter wrote a blog post last year discussing why he no longer contributes to the site. Richter had been a member for four years, scored over 14,000 points in the gaming system, and was in the top 3 percent of overall contributors. However, he came to feel that StackOverflow had problems with its pedagogy and scoring system.
I disagree. StackOverflow’s format and rewards system may not appeal to all, but I’ve found it useful more times than I can count. It’s one of the only places to gather information about niche, deeply technical issues, and get specific, case-by-case help.

Put Your Hobby Code on GitHub

Developers grow by reading the source code of others and building on it. This is how progress and innovation have happened since the dawn of time. Receiving constructive feedback for your work and drawing inspiration from the work of others is the best way to get better, whether you are talking about writing a novel, designing a building or building an app. When it comes to code, GitHub is the best place to learn, share and improve.
Truth be told, GitHub still hasn’t hit on the right way to build a social presence, as opposed to LinkedIn, which is doing it right in small increments. You can publish blog posts on LinkedIn now and they become a lasting part of your profile. I predict that GitHub will end up supporting something like that, too. In the meantime, it’s a great free resource for collaborating on code and learning from the best.

Create Positive and Productive Work Environments

Startups often expect their employees to work for a lower salary in anticipation of larger equity rewards down the line, but this limits the available hiring pool. Many developers, such as those with kids, may not want to take on that financial risk. Weeby, in an effort to attract the best-and-the-brightest away from competitors, is offering “epic salaries.”
Software development is an individual and creative endeavor. It has more in common with sculpting than with, say, accounting or HR. Employers have been slow to recognize this, but if Weeby’s experiment is successful, we may see more employers appreciating just how integral developers are to an organization’s success. This isn’t about high salaries, but about creating positive and productive work environments where developers can thrive.

White House Report Sees Potential, Pitfalls Of Big Data

A new report released by the White House today outlines the potential and pitfalls of big data in our lives. While there is tremendous economic and social promise from big data, there is also equal prospect for abuse, especially when it comes to privacy and personal data protection.
President Obama plans to file several pieces of legislation in the coming months around consumer privacy and protection, data breach reporting and protection of school children’s data.
Last January, the president asked John Podesta, counselor to the president, to lead a working group to look into the implications of Big Data. At the same time, the President’s Committee of Advisors on Science and Technology was also looking into the matter on a more technical level. Both teams have filed initial reports, Podesta explained at a White House briefing this morning.
“Both of those reports concluded that we live in a world of near ubiquitous data collection, where data is being crunched at speeds increasingly approaching real time,” Podesta said.
Big data as a technology represented a tremendous opportunity to transform healthcare, boost economic productivity, empower consumers and make government work better, saving taxpayer dollars in the process, he added.
“But at the same time. those same technologies raise concerns about how protect personal privacy and other important values. As more data is collected, analyzed and stored on both public and private systems, we need to be vigilant to ensure the balance of power is retained between government and citizens and between businesses and consumers, he said.”
In a case of perfect timing, just this morning, Anthem, the nation’s second largest insurer reported a major security breach. One of the recommendations in today’s report is legislation around how companies should report breaches of this very type.
But of course, these breaches aren’t new. Whether it’s Sony, Home Depot, JP Morgan or Target to name a few of the higher profile cases, these breaches have been happening with startling regularity.
Responding to a question about the Anthem breach, Podesta said that it sounded like the company was responding in a timely manner and was “operating in a realm in what we view as best practice.”
But the purpose of legislation would be to create a consistent set of responses. “We want to see consistent application and high set of standards for consumers and then redress of consumers,” Podesta explained.
It’s important to remember that in any type of legislative proposal, even one involving cybersecurity or big data, politics is going to play a role with any plan originating from the White House. One area that could find broader bipartisan support is legislation protecting information collected about school children, especially while they are at school.
The president has proposed legislation around school data privacy and has found a sponsor from both sides of the aisle to advance it. Information mined from students while interacting with technology at school “shouldn’t be mined for marketing or commercial activities,” Podesta said. He believes that’s something both Republicans and Democrats can get behind.
It might be more difficult to find common ground around consumer protection legislation as it related to big data privacy, Podesta admitted, but he expressed hope that they could find bipartisan sponsors. He added, they had not completely drafted the language of that bill and it was still in progress.
Another problem that needed scrutiny was around big data and the ability to apply discriminatory pricing on the fly using data businesses glean about individual buyers, Jason Furman, who is Chairman of the Council of Economic Advisors, explained at the briefing.
Differential pricing, much like big data, can be positive or negative depending on how its applied. Furman used the example of offering children and seniors cheaper movie tickets. In this case, he says, the theater is offering a better price to groups who have less economic clout to draw them into the theater.
On the flip side, an airline might charge a higher price to a business person looking for a flight at the last minute because this consumer probably has the money and is willing to pay it.
They aren’t concerned with areas where businesses use pricing in this manner, and he was careful to point out that big data has the potential to empower consumers, and ideally offer them ways to protect information they didn’t want to share.
But it can get tricky, especially in higher stakes transactions such as employment, insurance and credit, where he said there was substantial concern regarding privacy, data quality and fairness.
“In these settings, big data can facilitate problematic practices, many of which are covered and would run afoul of existing laws like the Fair Credit Reporting Act and The Civil Rights Act,” Furman explained.
He pointed out that big data works both ways in this instance because it’s also a tool that can be used by regulators to weed out questionable or illegal practices.
The report and today’s briefing showed that big data, as any technology, can be used for good or harm, depending on how it’s applied.
The president clearly recognizes these conflicting applications and he is trying to tamp down on the negative aspects while encouraging the positive. From here, it becomes part of the political theater in Washington, but it’s worth noting that these are all valid concerns about a developing technology like big data.
WordBoard’s New iOS 8 Keyboard Lets You Save Email Templates, Hashtags And More

Ever since Apple introduced support for third-party keyboards in iOS 8, developers have been racing to offer users more functionality than what’s provided by the stock keyboard alone, whether that’s better predictive typing, support for GIFs or different input methods like Swype. A new keyboard app launching today, WordBoard, is instead focused on saving you from having to type the same things over and over, including standardized emails.
The app was developed by Stuart Hall, whose company Bytesize today has a number of iOS applications on the iTunes App Store, both free and paid. The largest of these, the “7 Minute Workout” app, was downloaded 2 million times, and was recently acquired by Wahoo Fitness.
With WordBoard, he says the idea is to allow users to personalize and program their keyboards with regularly used information, like your email address, mailing address, phone number, favorite hashtags for use on social media, ASCII art or even email template replies.
While there are a few keyboard apps that allow you to save commonly used information or favorite phrases – we’ve looked at OftenType and PhraseBoard before, for example – WordBoard’s support for email templates could see it appealing more to business users than consumers. With the ability to save longer, customized emails like sales templates, customer support responses, or even just different email signatures for your many hats, WordBoard could prove useful for those who run their businesses from their mobile phones.
For consumers, there’s also a paid feature that lets you import your hashtags from Twitter and Instagram, in order to set up personalized “boards” with your favorite tags. This is available for an in-app purchase of $1.99, which also gives you the option to import contacts and create an unlimited number of keys.
Since the free version includes only up to six keys, most will likely want to upgrade in order to utilize WordBoard’s full functionality. (In a way, the free download basically allows you to test the app before committing to buy.)
As with most iOS 8 keyboards, you’ll have to give the app full access in settings in order for the form-filling features to work after installation. The company clarifies it only does this to share data between the app and keyboard, and doesn’t use other features that “full access” enables, such as network access.
The app is available here on iTunes, and makes a decent addition to your lineup of extra keyboards.

After Raising $1.3M On Indiegogo, Airtame Closes $1.4M Seed Funding To Scale Up Wireless HDMI Dongle

Investors are wont to follow. It therefore shouldn’t be a surprise to see Airtame pick up a VC round of funding.
The Copenhagen-based startup, which is building a nifty wireless HDMI dongle to easily share your computer or phone’s screen to a TV or projector, made headlines in late 2013 for its crowdfunding efforts after raising $1.3 million on Indiegogo in just 60 days.
To add to that pot of cash, the company has closed a $1.4 million seed round led by Danish investment firm SEED Capital and Libratone-founder Tommy Andersen — money it plans to use for a full product launch in the second quarter of this year.
airtame-dongle-2d-2-2That’s not to say that Airtame devices haven’t already begun shipping. Specifically, I’m told that, of the 15,000 pre-orders that the startup’s Ingiegogo campaign garnered, just over 3,000 units have already shipped to backers, providing valuable feedback to the company as it readies to scale up.
And scaling up is the name of the game here. When you smash through your crowdfunding target in the way that Airtame did, it creates a new set of problems, albeit nice problems to have. Namely, how to scale up manufacturing much faster than originally planned.
“Even though being over-funded is awesome, there’s some downsides to it as well,” Airtame co-founder and CEO Jonas Gyalokay tells me. “In short it can be summarised by the fact that scaling fast is extremely hard – and takes time. Almost all of the over-funded hardware projects get delayed, and I think there’s several reasons for that.”
These include the fact that “hardware is hard” and after receiving so many preorders, your original preparation “goes out the window”. “Entrepreneurs don’t heed warnings,” adds Gyalokay.
To that end, since Airtame’s Indiegogo campaign finished, it’s grown the team from 6 to 17 people, mostly in the area of software engineering. The startup has also signed a partnership with Jabil (the world’s 3rd largest electronics manufacturer), which has enabled it to start ramping up production.

ClusterHQ Raises $12M Series A Round To Expand Its Container Data Management Service

ClusterHQ today announced that it has raised a $12 million Series A round led by Accel Partners London, with participation from Canaan Partners and existing investors.
The company may not be a household name yet, but its Flocker tool has gotten quite a bit of attention among developers because it makes it easier to move apps that run in Docker containers and their data. Almost by default, Docker is more about handling stateless services — that is, the application logic and not the data.
Whenever you shut down a Docker container, after all, all the data stored in it is lost. Flocker expands the Docker ecosystem by giving developers a tool for managing data volumes in Docker clusters and making them as portable as their Docker containers. It supports many of the most popular databases, key-value stores and message queueing services and runs on most cloud computing platforms, with support for CoreOS, Cloud Foundry and Mesosphere coming soon.
flocker-architecture-diagram
Besides Flocker, the company is also working on Powerstrip, a tool for building prototype Docker extensions.
The company raised a $1 million seed round in 2013, just around the time the hype around containers got started. Its CEO Mark Davis previously co-founded Virsto Software, a storage service that was acquired by VMware in 2013. ClusterHQ co-founder and CTO Luke Marsen was previously an infrastructure engineer at TweetDeck.
Davis tells me that the company’s business model will be quite similar to that of other open-source companies in that ClusterHQ will launch a number of paid tools and consulting services in the long run. It’s no surprise then, that the company plans to use its funding to expand its technical and go-to-market resources. Davis notes that the team is working on building more features into Flocker and that his company is “actively working with the community on a number of projects and will have more to say about partnerships in the future.”

Message Systems Buys Rival Port25 Solutions To Create Email Infrastructure Giant


In a marriage of two email infrastructure rivals, Message Systems bought Port25 Solutions today for an undisclosed mix of stock and cash. With it, they have created a company that covers every email infrastructure need from small business all the way to mega messaging clients like social networks.
Message Systems CEO Phillip Merrick, says the acquisition gives his company unmatched coverage. It plans to incorporate Port25 as a stand-alone business unit inside Message Systems devoted to medium-to-large sized markets.
When I started looking at this deal, I mistakenly thought these companies might help deliver spam emails, but Merrick pointed out to me in an email exchange, that their services are about helping large organizations like Facebook, PayPal, financial institutions and so forth, deliver huge volumes of legitimate email to their constituencies, while ensuring the email actually hits its target.
“This is absolutely in the category of wanted email,” Merrick explained. “Everything from fraud alerts from your credit card company to the LinkedIn and Twitter digests you receive. Plus the newsletters you sign up for, and the retail promotions where you have specifically opted in.”
He added that his company works with others to help prevent spam and malicious emails.
“We have worked with major customers such as Twitter and LinkedIn, in conjunction with Google and others, to implement email security standards that make spam and phishing attacks far more difficult,” he said.
Message Systems’ roots as an independent company date back to 2008, but prior to that it was developed and sold by a consulting company. In total, Message Systems has been offering these services for over 15 years. Merrick says his company has been so successful in this space, he claims it moves 23 percent of the world’s legitimate email, and now with the acquisition of Port25, that number will be even higher.
With Port25, Message Systems gets its 1,000 customers, which include Salesforce’s marketing cloud, CNN, New York Times Digital and many others. It also obtains a contrasting product that companies can download and install without a lot of help. Message Systems is installed in the data center and that usually involves a more complex implementation.
Port25’s CEO, John C. Karpovich explained that combining the two companies brings a range of services that would not have been possible, had they remained stand-alone entities.
“While Port25 built and was very successful at selling an easy-to-use on-premise email product (mostly to medium-to-large senders), with the two companies combined, we now have email infrastructure offerings for senders of any size — from small to mega large senders in their choice of deployment — on-premise and in the cloud,” he wrote in an email.
But perhaps the underlying reason behind this purchase was a classic case of trying to stave off disruptive forces in the marketplace — in this case, SendGrid, a cloud-based email infrastructure startup making waves in the market. SendGrid doesn’t have a huge market in terms of message volume — around two percent, according to the company website — but it’s picking up many of the emerging startup business such as Uber, Pinterest and Spotify and this is an area Message Systems very badly wants. According to SendGrid, that two percent marketshare adds up to 14 billion emails per month.
“We obviously want to maintain our leadership and transfer leadership in data center technology to the cloud and SendGrid has an interesting start with about [180,000] startups using their platforms,” Merrick said.
While Message Systems has a cloud offering called SparkPost, which Merrick pointed out has been doing very well, both companies are primarily on-premise offerings. Merrick hopes to change that by expanding its cloud coverage moving forward, presumably to put it in a better position to keep SendGrid at bay.
Message Systems has raised $38M in two rounds, the most recent being $32M in Series B in June, 2012. Port25 Solutions has been around since 1999 and never taken any funding.
Coincidentally, Merrick says, the two companies are only four miles from one another just outside of Washington, D.C. Message Systems also has a San Francisco office. Message Systems, which has 150 employees, plans to incorporate all 13 Port25 employees as part of the deal.


Copyright @ 2013-2015 FB Display Picture.

Designed by Templateiy & CollegeTalks